Introducing Chainguard Harness: Proven Vulnerabilities and Ready-to-Merge Fixes From Frontier AI, No Model Access Required
Image File
Original HTML

Available through the Claude Marketplace by Anthropic, Harness unleashes frontier AI on a live, isolated build of an organization's application and delivers only proven vulnerabilities, each with a recommended fix ready to merge

SEATTLE, Oct. 14, 2026 /PRNewswire/ -- Chainguard, the trusted source for open source, today announced Chainguard Harness, a new cyber harness that uses frontier AI models like Anthropic's Claude Mythos 5.1 to find and fix exploitable vulnerabilities in an organization's application code. Harness builds an application from an organization's source code in an isolated microVM, instructs a frontier model to hunt for exploitable vulnerabilities in a live, running instance, and reproduces every finding before delivering a tailored, staff-reviewed fix. Teams benefit from frontier vulnerability hunting without needing their own access to frontier models, and act only on proven findings rather than sifting through noise. Chainguard Harness is now available in the Claude Marketplace, so customers can purchase Harness directly from Anthropic and consolidate their AI spend.

Finding vulnerabilities is no longer the hard part

Frontier AI models have become remarkably effective at finding and chaining exploitable vulnerabilities, but most organizations cannot put that capability to work on their own code. Access to frontier models that perform vulnerability discovery across first-party and open source code has been mostly available to a select group of organizations performing defensive security work for critical infrastructure. Traditional scanners add to the problem: they analyze static code, flag issues that may never be reachable, and miss the logic flaws, injection paths, and resource exhaustion bugs that only appear when an application is actually running. The result is a growing backlog of unverified alerts, with engineers spending hours and tokens triaging findings and writing their own patches instead of shipping. Chainguard Harness closes the gap by finding exploitable, reproducible vulnerabilities and providing fixes for both open source and first-party code.

"Every time we've pointed Harness at code, it has found serious, exploitable vulnerabilities, including in software that's been scanned many times over and code that runs critical infrastructure," said Dan Lorenc, CEO and Co-founder, Chainguard. "That capability is beginning to make its way to more and more organizations, and the teams that move first will be the ones that find and fix these issues before they become incidents. Harness offers another option for security teams to get proven vulnerabilities and fixes their engineers can ship."

Proven vulnerabilities, with fixes written for your code

Chainguard Harness connects to a team's repository through the Guardener GitHub app, builds the application exactly as it ships, and boots it in an isolated microVM. A frontier model then probes the live application for exploitable vulnerabilities, testing it in context, the way an attacker would, rather than reading static code. Every finding is replayed in a fresh, isolated environment until it reproduces every time, so teams only see what is proven. When a vulnerability is confirmed, Chainguard delivers reliable reproduction steps alongside a fix written for that specific codebase.

Chainguard Harness includes:

- Frontier AI without frontier access: Teams get the benefit of frontier-model vulnerability hunting on their own applications without needing their own access to frontier models.

- Built for the bugs that live at runtime: Harness tests a running copy of the application instead of just static code, surfacing logic flaws, injection, and resource exhaustion that only show up in context.

- Isolation by design: Every run happens in its own microVM sandbox built from source on Chainguard OS, with no network egress, no credentials inside, and full audit logging.

- Reproducible, verified findings: Every finding is replayed in a fresh, isolated environment until it lands every time, reducing false positives and security noise.

- Fixes written for your code: Custom recommendations across first-party code and open source dependencies give teams a path to secure code, not a list of risks.

- Human review on every fix: A Chainguard engineer reviews and approves every fix and report before it reaches a customer.

- Responsible disclosure built in: Vulnerabilities found in open source go upstream to maintainers through Athena, Chainguard's coordinated vulnerability disclosure process.

At launch, Chainguard engineers operate Harness on behalf of customers by running it against the trusted open source artifacts Chainguard already distributes and delivers patched builds via Chainguard Repository, and by running it against a customer's source code and delivering an engineer-reviewed report of validated findings with severity, impact, reproduction steps, and recommended remediation.

Available through the Claude Marketplace by Anthropic

Chainguard Harness is available through the Claude Marketplace by Anthropic, allowing enterprises to use a portion of their existing Anthropic commitment to procure it. Chainguard Harness reproduces vulnerabilities discovered by Mythos 5.1 in an isolated environment, ensuring every fix is reviewed by a Chainguard engineer, and sharing results that customers can act on immediately. Anthropic manages invoicing, so Anthropic customers can add Harness without a separate procurement process and consolidate their AI spend.

"Models like Claude Mythos 5.1 can surface vulnerabilities that have gone unnoticed for years, so how that capability is deployed matters as much as the capability itself," said Daniela Hurtado, Head of Commercial Cyber, Anthropic. "Chainguard Harness surrounds Mythos 5.1 with isolation, reproduction, and human review, so defenders get the benefit, and every finding is verified before it reaches a customer. Through the Claude Marketplace, enterprises can put their existing Anthropic commitment directly toward that kind of risk reduction."

Chainguard Harness is available through a beta waitlist. To learn more, visit www.chainguard.dev/harness.

About Chainguard

Chainguard is the trusted source for open source. By providing engineers and AI agents with hardened, trusted, and production-ready artifacts, Chainguard helps organizations prevent AI supply chain attacks, increase engineering velocity while reducing toil, and maintain continuous compliance. Customers include Fortune 500 enterprises and global industry leaders, including Anduril, Canva, DocuSign, OpenAI, Public Storage, Snap Inc., and Snowflake. Chainguard is venture-backed by leading investors, including Amplify, IVP, Kleiner Perkins, Lightspeed Venture Partners, Mantis VC, Redpoint Ventures, Sequoia Capital, and Spark Capital.  For more information, visit: https://www.chainguard.dev/ 

Media Contact: Brittany Hendrickson, [email protected]

SOURCE Chainguard

Share this article
Class (B2B/B2C)
B2B
Ingest Status
Rewritten
Dedupe hash
prn_302907725
Press Eligible
Yes
Press Eligible Reason
Chainguard announced an enterprise cybersecurity product for AI-driven vulnerability detection and remediation.
Source Name
Introducing Chainguard Harness
Original Summary

<p>Available through the Claude Marketplace by Anthropic, Harness unleashes frontier AI on a live, isolated build of an organization's application and delivers only proven vulnerabilities, each with a recommended fix ready to merge SEATTLE, Oct. 14, 2026 /PRNewswire/ -- Chainguard, the...</p>

Image URL
https://mmx.prnewswire.com/media/MS684620/Chainguard-Logo.jpg?id=OA3017490&p=facebook
Content Hash (SHA-256, erste 32 hex)
a960aef470cdb41ddbe2f8757dc00559
Princeton Digital Group Receives Frost &amp; Sullivan's 2026 Asia-Pacific Customer Value Leadership Recognition for Data Centre Infrastructure and Operations Excellence
Original HTML

Princeton Digital Group Receives Frost & Sullivan's 2026 Asia-Pacific Customer Value Leadership Recognition for Data Centre Infrastructure and Operations Excellence

Customer-centric infrastructure strategy, technology flexibility, operational discipline, and scalable growth strengthen PDG's position in Asia Pacific's rapidly evolving data centre landscape.

SAN ANTONIO, Oct. 14, 2026 /PRNewswire/ -- Frost & Sullivan is pleased to announce that Princeton Digital Group (PDG) has earned the 2026 Asia-Pacific Customer Value Leadership Recognition in the data centre infrastructure and operations industry for its strong performance in customer value creation, strategic execution, technology leverage, and operational excellence. The recognition highlights PDG's ability to align infrastructure investment with evolving hyperscale customer requirements while delivering consistent value across diverse APAC markets.

Frost & Sullivan evaluates companies through a rigorous benchmarking process across two core dimensions: strategy effectiveness and strategy execution. PDG demonstrated strength across both, aligning its growth strategy with customer demand while executing with consistency across markets where infrastructure maturity, regulations, power availability, and construction ecosystems vary significantly.

"PDG has built customer value into the way it makes infrastructure, technology, and investment decisions. Its approach goes beyond delivering capacity; it demonstrates a clear understanding of how reliability, flexibility, and operational discipline influence the long-term infrastructure decisions of hyperscale customers," said Gautham Gnanajothi, Senior Vice President at Frost & Sullivan.

PDG's customer engagement model begins well before contracts are signed. The company works closely with customers on capacity planning, sharing market- and cluster-level visibility into planned supply while incorporating customers' forward demand outlook into investment priorities. Upstream engagement continues through execution, with PDG adapting technical requirements to APAC market conditions and identifying alternative technology and equipment options when necessary.

Technology adoption is similarly guided by customer requirements rather than novelty. PDG has focused on building reliable, repeatable scale across its markets, including supporting the transition of liquid cooling from limited deployments to broader, hyperscale requirements. Its willingness to evaluate additional OEM options has helped expand the pool of viable suppliers and support scalable deployment across a portfolio approaching two gigawatts of capacity at the time of assessment.

PDG approaches "AI-ready" infrastructure as an operational requirement rather than a marketing concept. Its engineering and commercial flexibility allows projects to accommodate changing cooling requirements during construction without allowing uncertainty to delay delivery. The customer-centric approach is complemented by investments in operational efficiency, where improvements such as power usage effectiveness can translate directly into customer value.

"What differentiates PDG is our ability to deliver at scale across some of Asia Pacific's most complex and fast-growing markets. We combine deep in-country expertise with the scale and capabilities of a pan-APAC business and strong institutional capital backing, which allows us to move with speed and execute consistently. For hyperscalers, that combination matters as they build increasingly large and sophisticated infrastructure across the region. This recognition is a testament to our teams and the long-term partnerships we have built with our global customers," said Varoon Raghavan, COO and Co-Founder at Princeton Digital Group.

PDG's growth strategy reflects its focus on scalable customer value. Its expansion across APAC markets that include Mumbai, Jakarta, Johor, and Tokyo demonstrates an approach that adapts to local market conditions while maintaining consistent enterprise standards. Empowered local teams work alongside a central platform structure, enabling PDG to respond to market-specific requirements while sharing capabilities and expertise across countries.

Frost & Sullivan commends Princeton Digital Group for its customer-centric strategy, disciplined execution, technology flexibility, and ability to scale data centre infrastructure while maintaining a consistent focus on customer outcomes. The company's approach demonstrates how operational efficiency, human capital, technology adoption, and growth can work together to create sustainable value in APAC's data centre infrastructure market.

Each year, Frost & Sullivan presents the Customer Value Leadership Recognition to a company that demonstrates excellence in creating measurable value for customers through effective strategy development and execution. The recognition highlights organizations that demonstrate customer-centric innovation, strategic responsiveness, and sustained excellence within their respective industries.

Frost & Sullivan Best Practices Recognition

Frost & Sullivan's Best Practices Recognitions honor companies across regional and global markets that exhibit exceptional achievement and consistent excellence in areas such as leadership, technological innovation, customer experience, and strategic product development. Each recognition is the result of a rigorous analytical process in which Frost & Sullivan industry experts benchmark performance through comprehensive interviews, deep-dive analysis, and extensive secondary research. The goal is to identify true best-in-class organizations that are driving transformative growth and setting new industry standards.

Contact us: Start the discussion.

Contact:

Tarini Singh

E: [email protected]

About Princeton Digital Group (PDG)

Princeton Digital Group (PDG) is a leading developer and operator of data centers. Headquartered in Singapore with operations in Singapore, Japan, India, Indonesia, China, Malaysia, South Korea, and Australia, its portfolio of data centers powers the growth of AI and cloud across Asia Pacific. For more information, visit www.princetondg.com or follow us on LinkedIn.

SOURCE Frost & Sullivan

Share this article

Class (B2B/B2C)
B2B
Ingest Status
Rewritten
Dedupe hash
prn_302903851
Press Eligible
Yes
Press Eligible Reason
Company recognition highlights data centre infrastructure, operations, and growth strategy.
Source Name
Unknown Company
Original Summary

<p>Customer-centric infrastructure strategy, technology flexibility, operational discipline, and scalable growth strengthen PDG's position in Asia Pacific's rapidly evolving data centre landscape. SAN ANTONIO, Oct. 14, 2026 /PRNewswire/ -- Frost & Sullivan is pleased to announce that...</p>

Content Hash (SHA-256, erste 32 hex)
998d01525e2ba716c05fb64db1d7b14e
Telix Highlights Pivotal Trials in Prostate, Brain and Renal Cancers and Next Generation Theranostics at EANM
Image File
Original HTML

Telix Highlights Pivotal Trials in Prostate, Brain and Renal Cancers and Next Generation Theranostics at EANM

MELBOURNE, Australia and INDIANAPOLIS, Oct. 14, 2026 /PRNewswire/ -- Telix Pharmaceuticals Limited (ASX: TLX, NASDAQ: TLX, "Telix") today announces that 20 company-related abstracts will be presented at the 39th Annual Congress of the European Association of Nuclear Medicine (EANM) to be held in Vienna, Austria from October 17-21, 2026.

Dr. David N. Cade, Telix Group Chief Medical Officer, said, "Our expansive presence at EANM reflects the breadth and maturity of Telix's pipeline, spanning pivotal therapeutic studies, precision diagnostics and next-generation technologies. The selection of 12 abstracts for top-rated oral presentations is a strong recognition of the quality and clinical relevance of this work. We look forward to continuing this discussion at our sponsored symposium on the future of theranostics in urologic oncology."

Key presentations include the Phase 3 IPAX BrIGHT trial of TLX101-Tx in recurrent glioblastoma, the Phase 3 LUTEON trial of TLX250-Tx in ccRCC, and interim results from the PTherpan-Lu trial of TLX597-Tx in mAPMR prostate cancer[1]. Topline Phase 3 data for TLX591-Px (Illuccix) PET[2] imaging of prostate cancer in Chinese men will also be presented, together with real-world experience with TLX250-Px (Zircaix[3]) in ccRCC, and research from our targeted alpha therapy and MedTech programs. As in previous years, Telix will support the EANM Sanjiv Sam Gambhir Young Investigator Award, in memory of an extraordinary man and inspiring educator.

Visit booth #527 to explore opportunities for collaboration with Illuccix® (kit for the preparation of gallium-68 gozetotide injection), Telix's commercial PSMA-PET imaging[4] agent in Europe; our theranostic pipeline; and our medical technologies, including the SENSEI® miniature drop-in gamma probe, QDOSE® dosimetry software and artificial intelligence (AI).

EANM presentation details are as follows (all times CEST):

Sponsored Symposium

Title: The future doesn't wait: The next era of theranostics in urologic oncology.

Date & Time: 18-Oct-26, 13:15 – 14:45

Location: Hall F2, Austria Center Vienna

Chair: J. Calais, Gustave Roussy, IGR and Université Paris-Saclay, Paris, France

Agenda:

The theranostic revolution

- J. Calais

The evolving role of PSMA-PET in prostate cancer

- K. Herrmann, University Hospital Essen, Germany

- M. Ghesani, United Theranostics, USA

Next-generation PSMA therapeutics: Overcoming today's challenges

- D. Oprea-Lager, Radboud University Medical Center, Nijmegen, the Netherlands

- L. Emmett, St Vincent's Hospital, Sydney, Australia

Panel discussion - all

Extending prostate cancer theranostic success to broader GU diseases

- J. Calais

Oral presentations

Title: ELEGANCE, Prospective pilot study, assessing imaging performance of TLX250-Px ([⁸⁹Zr]Zr-girentuximab) PET/CT in Patients with Hepatocellular Carcinoma, Biliary Tract Cancer or Gastro-Entero-Pancreatic Neuroendocrine Neoplasms (NCT06735560)

Date and Time: 18-Oct-26, 08:00 – 09:30

Presenter: Clement Bailly, CHU Nantes

Abstract #: OP-036

Title: HIMIKO, TLX591-Px ([⁶⁸Ga]Ga-PSMA) PET/CT in Hepatocellular Carcinoma: impact of Multiparametric dynamic whole-body imaging and kinetic modelling (NCT06999837)

Date and Time: 18-Oct-26, 08:00 – 09:30

Presenter: Rachel Bardy, CHU Nantes

Abstract #: OP-041

Title: Exploring carbonic anhydrase IX as a diagnostic imaging target using TLX250-Px ([⁸⁹Zr]Zr-girentuximab) in Von Hippel-Lindau Disease: preliminary results from the CAT-VHL Phase 2 trial (NCT07171905)

Date and Time: 18-Oct-26, 15:00 – 16:30

Presenter: Fabrizia Gelardi, San Raffaele Hospital

Abstract #: OP-168

Title: LUTEON, Phase 3 study to assess safety and efficacy of TLX250-Tx (¹⁷⁷Lu-girentuximab) in advanced, relapsed or recurrent ccRCC (NCT07197580)

Date and Time: 18-Oct-26, 15:00 – 16:30

Presenter: Ghoufrane Tlili, CHU Bordeaux

Abstract #: OP-170

Title: Building the traceability backbone for radiopharmaceutical therapy, first results from the PDIB Secondary Standards Laboratory Network

Date and Time: 19-Oct-26, 08:00 – 09:30

Presenter: Steven Graves, University of Iowa

Abstract #: OP-291

Title: Optimizing SPECT/CT for alpha emitters: Phantom validation and calibration of [²¹¹At] imaging

Date and Time: 19-Oct-26, 08:00 – 09:30

Presenter: Rob van Rooij, UMC Utrecht

Abstract #: OP-294

Title: IODO-RISE, TLX101-Tx (iodofalan-¹³¹I) in recurrent high-grade glioma, investigation of safety and efficacy

Date and Time: 19-Oct-26, 08:00 – 09:30

Presenter: Tim Sturre, UMC Utrecht

Abstract #: OP-311

Title: IPAX BrIGHT, Pivotal study of TLX101-Tx (iodofalan-¹³¹I) with or without lomustine vs lomustine alone for the treatment of patients with radiographically confirmed recurrent glioblastoma at first recurrence (NCT07100730)

Date and Time: 19-Oct-26, 08:00 – 09:30

Presenter: Nelleke Tolboom, UMC Utrecht

Abstract #: OP-312

Title: Comparative evaluation of TLX252-Tx ([²²⁵Ac]Ac-) and TLX250-Tx ([¹⁷⁷Lu]Lu-DOTA-hG250) targeted radionuclide therapy and combination with PD1 blockade in a preclinical renal cell carcinoma model

Date and Time: 19-Oct-26, 16:45 – 18:15

Presenter: Twan van der Werff, UMC Radboud

Abstract #: OP-478

Title: Interim results from PTherpan-Lu trial: TLX597-Tx ([¹⁷⁷Lu]Lu-panPSMA) radionuclide therapy for patients with mCRPC[5]

Date and Time: 19-Oct-26, 16:45 – 18:15

Presenter: Yehia Omar, Misr Radiology

Abstract #: OP-523

Title: Integration of spatial analysis and deep learning for enhanced tumor classification in total-body PET/CT imaging: using residual deep learning with spatial feature augmentation and cross-validated ensemble learning

Date and Time: 20-Oct-26, 09:45 – 11:15

Presenter: Simon Wail, Telix Pharmaceuticals

Abstract #: OP-613

Title: TLX250-Px ([⁸⁹Zr]Zr-girentuximab) PET/CT for characterization of indeterminate renal masses, diagnostic performance and clinical impact in a real-world cohort

Date and Time: 20-Oct-26, 09:45 – 11:15

Presenter: Sazan Rasul, Medical University of Vienna

Abstract #: OP-627

ePosters

Title: QDOSE® allometry-guided human dosimetry of TLX102-Tx ([²¹¹At]APA): Impact of administration route on maximum tolerated activity

Abstract #: EP-0067

Title: Illuccix China, preliminary results from Phase 3 trial of TLX591-Px (⁶⁸Ga-PSMA-11) PET for detection of biochemical recurrence of prostate cancer in Chinese men (NCT05847348)

Abstract #: EP-0460

Title: TLX250-Px (⁸⁹Zr-girentuximab) PET/CT in Von Hippel Lindau disease; initial real-world experience in VHL expert center

Abstract #: EP-0595

Title: TLX250-Px (⁸⁹Zr-girentuximab) PET/CT in clear cell renal cell carcinoma, impact on staging and clinical management

Abstract #: EP-0599

Title: Impact of TLX250-Px (⁸⁹Zr-girentuximab) based radionuclide imaging in patients with renal cell carcinoma on virtual tumor board decision making

Abstract #: EP-0606

Title: A semi-mechanistic population biodistribution model of TLX250-Px (⁸⁹zr-girentuximab) for the diagnosis of clear cell renal cell carcinoma

Abstract #: EP-0999

Title: Potential for radioguided surgery based on internal conversion electron detection using a compact CMOS detector

Abstract #: EP-1070

Title: A dosimetric study of bladder endocavitary therapy using astatine-211

Abstract #: EP-1239

About Telix Pharmaceuticals Limited

Telix Pharmaceuticals (ASX: TLX, NASDAQ: TLX) is a commercial-stage global radiopharmaceutical company, advancing targeted theranostics to improve outcomes for people with cancer across the patient journey. Theranostics pairs a precision diagnostic with a targeted therapy to both diagnose and treat disease.

Telix's commercial franchise is anchored by its precision diagnostics portfolio: Illuccix® (kit for the preparation of gallium-68 gozetotide injection), commercially available in 22 countries including the U.S., and Gozellix® (kit for the preparation of gallium-68 gozetotide injection), approved by the U.S. Food and Drug Administration (FDA) for prostate imaging, and Pixclara® (floretyrosine F 18) approved by the FDA for glioma imaging. The Company's late-stage therapeutic pipeline includes three investigational assets in pivotal-stage trials: TLX591-Tx (lutetium-177 (177Lu) rosopatamab tetraxetan) in prostate cancer, TLX101-Tx (iodofalan 131I) in recurrent glioblastoma, and TLX250-Tx (lutetium (177Lu) girentuximab tetraxetan) in kidney cancer, additionally complemented by a deep pipeline of next generation candidates.

Telix is headquartered in Melbourne, Australia, with operations across North America, Europe, Latin America and Asia-Pacific. For more information, visit www.telixpharma.com or follow Telix on LinkedIn,X and Facebook.

Investor Relations

Annie Kasparian 

[email protected] 

Charlene Jaw

[email protected] 

Media

Eliza Schleifstein

917.763.8106 (Mobile)

[email protected] 

Legal Notices

Cautionary Statement Regarding Forward-Looking Statements. 

You should read this announcement together with our risk factors, as disclosed in our most recently filed reports with the Australian Securities Exchange (ASX), U.S. Securities and Exchange Commission (SEC), including our Annual Report on Form 20-F filed with the SEC, or on our website.

The information contained in this announcement is not intended to be an offer for subscription, invitation or recommendation with respect to securities of Telix Pharmaceuticals Limited (Telix) in any jurisdiction, including the United States. The information and opinions contained in this announcement are subject to change without notification. To the maximum extent permitted by law, Telix disclaims any obligation or undertaking to update or revise any information or opinions contained in this announcement, including any forward-looking statements (as referred to below), whether as a result of new information, future developments, a change in expectations or assumptions, or otherwise.

Class (B2B/B2C)
B2B
Ingest Status
Rewritten
Dedupe hash
prn_302907930
Press Eligible
Yes
Press Eligible Reason
Company news on clinical trials and radiopharmaceutical research presented at a medical congress.
Source Name
Unknown Company
Original Summary

<p>MELBOURNE, Australia and INDIANAPOLIS, Oct. 14, 2026 /PRNewswire/ -- Telix Pharmaceuticals Limited (ASX: TLX, NASDAQ: TLX, "Telix") today announces that 20 company-related abstracts will be presented at the 39th Annual Congress of the European Association of Nuclear Medicine (EANM) to be...</p>

Image URL
https://mmx.prnewswire.com/media/MS1385889/Telix-Main-Logo-Logo.jpg?id=OA3017841&p=facebook
Content Hash (SHA-256, erste 32 hex)
dc0e90db205361472eef211d5cd5ebd4
Chainguard Research: Nine in Ten Security Leaders Say AI Attacks Have Changed Their Job More Than Anything in a Decade, but the Ability to Act Hasn't Kept Pace
Image File
Original HTML

Survey of 1,300 security leaders finds 77% expect an attacker to exploit a vulnerability at their organization in the next year, while 54% say their companies knowingly leave high or critical vulnerabilities unpatched at least sometimes

KIRKLAND, Wash., Oct. 14, 2026 /PRNewswire/ -- Chainguard, the trusted source for open source, today released The AI Exploit Gap, a global report surveying 1,300 security leaders, that explores the widening distance between how fast AI-powered tools can find and chain vulnerabilities and how fast human teams can fix them. Nine in ten (91%) security leaders say AI-accelerated attacks have changed their job more than anything else in the past decade, and 77% believe it is likely an attacker will exploit a software vulnerability at their organization within the next 12 months. Yet 54% acknowledge their companies knowingly leave high or critical vulnerabilities unpatched at least sometimes, a sign that the ability to act hasn't kept pace with the speed of change.

AI is expanding risk, and leaders are feeling it

The same technology making engineers faster is also making defenders' jobs harder, and the pressure is landing on security leaders personally. Over half say burnout is affecting their team's ability to defend against those same threats. Security teams are facing a triple threat: frontier AI models finding vulnerabilities faster than ever, attackers using the same tools to exploit them, and supply chain attacks bringing in risk from outside the organization. Regulations, such as the EU Cyber Resilience Act and Product Liability Directive, are also adding to the pressure by raising the cost of leaving known vulnerabilities open. While engineering teams are on the frontlines of vulnerability remediation, security leaders, who are held responsible when a vulnerability is exploited, are often caught in the middle.

"AI has changed the security job faster than anything else in the past decade, and security leaders can see exactly where it's heading. Most we talked to expect an attacker to exploit a vulnerability in their organization this year," said Quincy Castro, Chief Information Security Officer, Chainguard. "But seeing the risk and being able to act on it are two different things. AI can find and chain flaws in minutes, while fixing them still moves at human speed and competes with product deadlines and uptime. That's the AI exploit gap, and it hits security and engineering teams in the areas where many historically struggled prior to AI. Thinking you'll just patch faster is the Red Queen talking. Patching faster isn't viable for most folks and it will consume increasing amounts of resources just to keep pace. The way out is for engineering and security to own the problem together and make prevention the standard, instead of just trying to run twice as fast."

Where the gap is widening

The data shows that many organizations view exploitation as probable even when leaders have confidence in their security programs. Among respondents who rated their cybersecurity tools as very effective, 77% still expected an attacker to exploit a vulnerability in the next year. The same was true for 78% of leaders who considered their incident response teams very equipped to handle AI-driven attacks, and 77% of those who said investments had stayed ahead of the threat. Other key findings include:

- AI threats are fueling burnout: 64% of security leaders say concern about AI-accelerated attacks contributed moderately or greatly to their own burnout in the past year. Nearly all respondents (96%) say security-team burnout has some impact on their organization's ability to defend against AI threats, and 54% describe that impact as moderate or significant.

- Machine-speed discovery is overtaking human-led remediation: 93% expressed concern that their companies cannot remediate AI-driven exploits quickly enough. More than half expect AI-powered vulnerability discovery to routinely outpace their teams within a year.

- Large and small companies face different barriers to patching: Companies with $1 billion or more in revenue leave high or critical vulnerabilities unpatched at more than twice the rate of companies with under $250 million in revenue (66% vs. 27% say they do so at least sometimes). Larger companies point to business trade-offs, such as revenue-generating work taking priority (46%) and patching being too disruptive to operations (48%), while smaller companies cite capacity constraints, such as difficulty testing patches (59%).

- Urgency is associated with lower exposure: Among leaders who believe AI already outpaces human remediation, 20% say their organizations leave critical vulnerabilities unpatched at least sometimes. That rises to 50% among those who expect AI to outpace remediation within a year and 64% among those who believe the shift is more than a year away.

- Teams are changing how they operate: 51% have reallocated staff to vulnerability remediation, 50% have adopted secure-by-default software components, 47% have reduced third-party dependencies, and 42% have increased scanning frequency. 40% have hired additional security staff, and 39% have added engineering staff.

- Organizations are continuing to spend: 70% say securing budget for AI-driven threat defense is easy, but 39% have bought tools they haven't rolled out. Only 22% rate their tools "very effective," and 77% of that group still expect an exploit in the next year. Nearly half (48%) say those investments still fall short of the protection boards and executive teams expect, and 93% believe senior leaders need to show greater urgency in addressing AI-accelerated threats.

The findings show security leaders aren't short on awareness or budget. What's missing is the ability to act at the speed AI now demands. Closing the AI exploit gap means treating prevention as the standard and making remediation a shared responsibility between engineering and security, so fewer vulnerabilities reach production in the first place.

Read the complete research findings here.

Methodology

This survey was commissioned by Chainguard and conducted by Wakefield Research, a third-party research partner, to collect responses from 1,300 cybersecurity leaders globally. Respondents were chosen from a variety of industries, and organization sizes and revenues. All respondents had a minimum seniority of Director, and worked for companies with at least 500 employees (except in Singapore and UAE/Saudi Arabia, where the minimum was 250 employees). Respondents were chosen from nine markets: U.S., U.K., France, Germany, Brazil, Singapore, Mexico, UAE/Kingdom of Saudi Arabia (KSA), and Japan, in September 2026, using an email invitation and an online survey.

About Chainguard

Chainguard is the trusted source for open source. By providing engineers and AI agents with hardened, trusted, and production-ready artifacts, Chainguard helps organizations prevent AI supply chain attacks, increase engineering velocity while reducing toil, and maintain continuous compliance. Customers include Fortune 500 enterprises and global industry leaders, including Anduril, Canva, DocuSign, OpenAI, Public Storage, Snap Inc., and Snowflake. Chainguard is venture-backed by leading investors, including Amplify, IVP, Kleiner Perkins, Lightspeed Venture Partners, Mantis VC, Redpoint Ventures, Sequoia Capital, and Spark Capital. For more information, visit: https://www.chainguard.dev/ 

Contact:

Brittany Hendrickson

[email protected]

SOURCE Chainguard

Share this article

Class (B2B/B2C)
B2B
Ingest Status
Rewritten
Dedupe hash
prn_302907743
Press Eligible
Yes
Press Eligible Reason
Cybersecurity research on AI-driven threats and enterprise vulnerability remediation.
Source Name
Chainguard Research
Original Summary

<p>Survey of 1,300 security leaders finds 77% expect an attacker to exploit a vulnerability at their organization in the next year, while 54% say their companies knowingly leave high or critical vulnerabilities unpatched at least sometimes KIRKLAND, Wash., Oct. 14, 2026 /PRNewswire/ --...</p>

Image URL
https://mmx.prnewswire.com/media/MS684620/Chainguard-Logo.jpg?id=OA3017502&p=facebook
Content Hash (SHA-256, erste 32 hex)
48a5bc1d744a85bc7148a86562eeb877
Huyett Expands into the Structural Steel Fastener Market with USA-Made A325 Bolts and More
Image File
Original HTML

Master distributor and manufacturer Huyett enters the structural market with an extensive inventory of parts, in stock and ready to ship in less-than-can quantities.

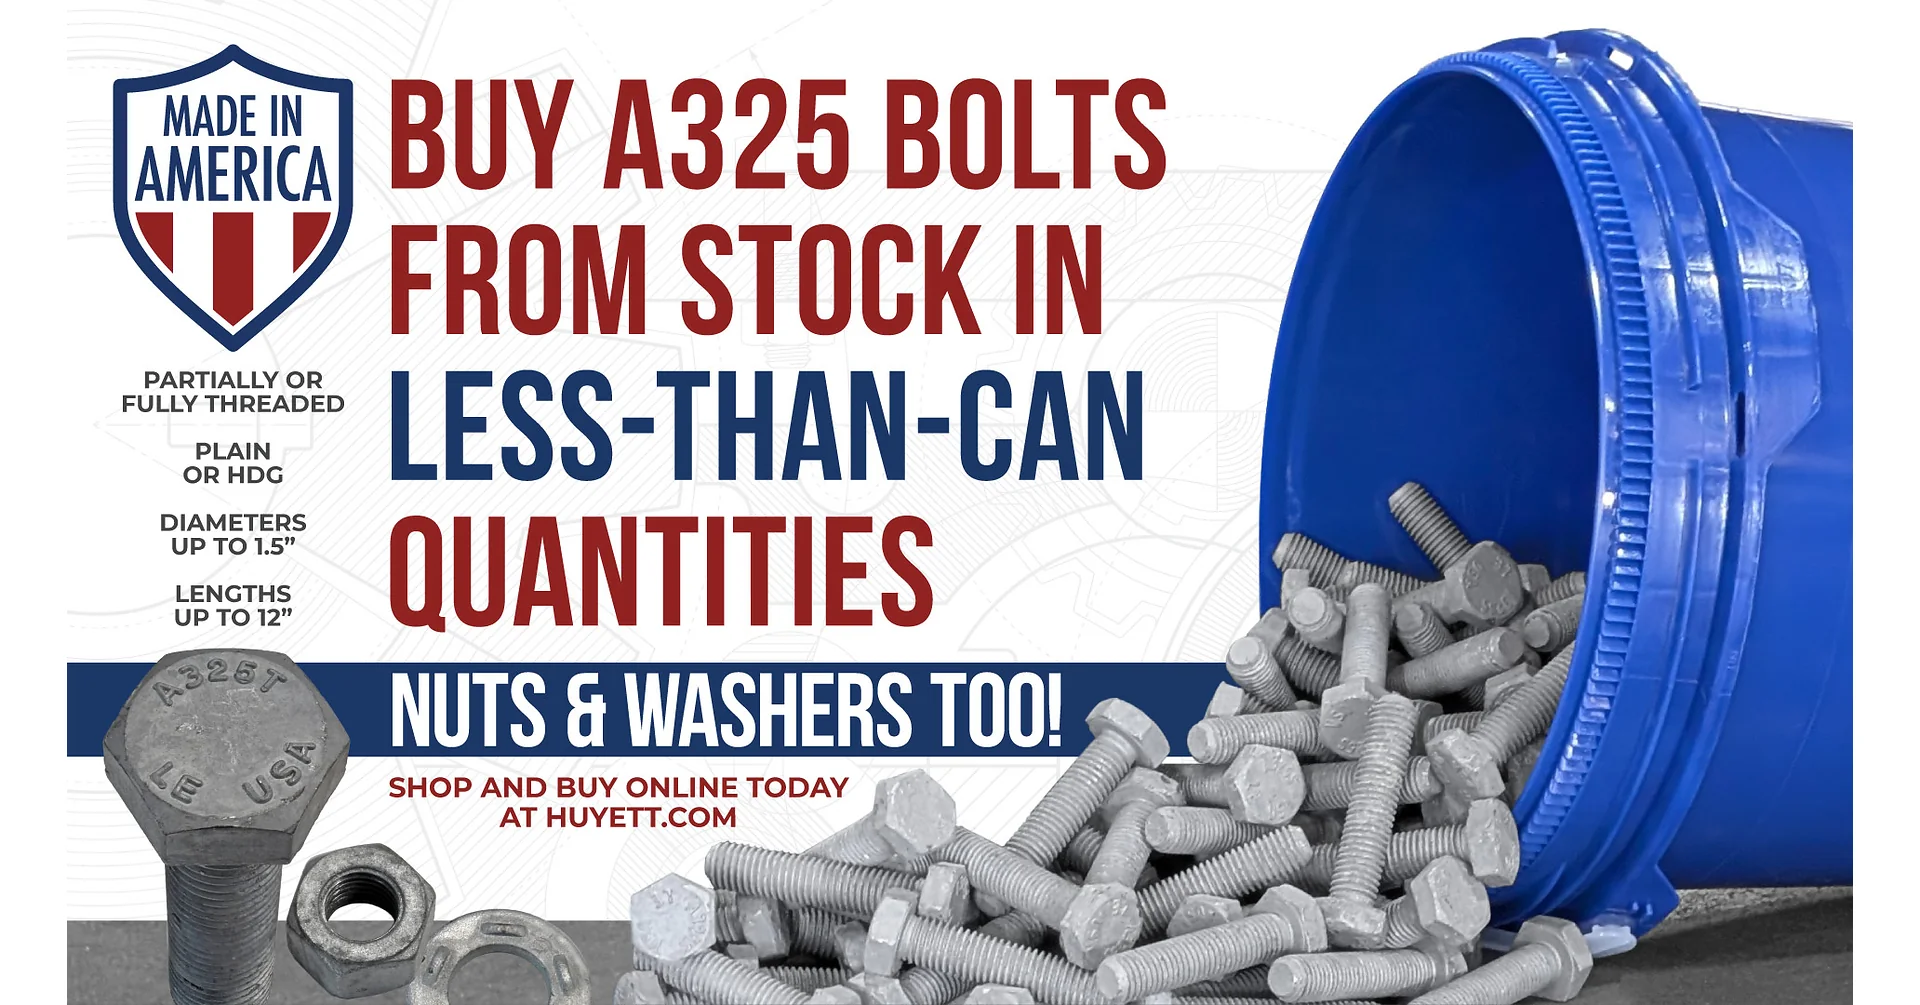
MINNEAPOLIS, Oct. 14, 2026 /PRNewswire/ -- Huyett is proud to announce its entrance into the structural bolting market with hundreds of items in stock in its La Porte, Texas location. Parts stocked by Huyett include A325 bolts, A563 DH nuts, A194 2H nuts, F436 washers, and Direct Tension Indicator washers (both standard and visual DTIs). Learn more at www.huyett.com/a325.

For Huyett, entering the structural fastener market is more than a strategic business expansion – it is an opportunity to fill key gaps in the industry. Huyett offers flexibility and convenience for customers by providing the following:

- Broken Cans: Huyett allows customers to purchase only what they need instead of overstocking.

- Full Threads: Huyett now offers America's most complete fully threaded structural bolt selection from stock. Fully threaded bolts are more versatile and can be cut to size to meet different application needs.

- Short Lead Times: In-stock items are available with same-day or next-business-day shipping, keeping production on track even in urgent situations.

- Made-in-America Inventory: A wide array of USA-made parts with plain and hot-dip galvanized finishes are available, helping customers meet country-of-origin requirements.

Expanding into the structural market with broken-can quantities and short lead times represents Huyett's commitment to Odd Parts. Odd Lots. On Time! – hard-to-find parts sold in quantities that make sense for your business, with fast shipping to ensure on-time delivery. In selling odd lots, Huyett gives the market access to high-quality structural products on an as-needed basis – customers can buy only what they need and get in-stock items fast.

"Odd Parts, Odd Lots, On Time is about the value we provide to our customers and our suppliers," said Timothy O'Keeffe, CEO of Huyett. "We fill a unique channel position as an effective outlet for large manufacturers, allowing us to support odd lots in this high-growth product line to customers who do not want to purchase full cans of product."

About Huyett

Established in 1906 by Guy Huyett in the "other Minneapolis," Huyett is one of the oldest continuously operating businesses in Kansas. The Company is a leading innovator of products and services geared to support industrial distributors in the fastener and premium lifting hardware sectors, delivered by customer-centric people operating in a Culture of Excellence.

SOURCE Huyett

Share this article

Class (B2B/B2C)
B2B
Ingest Status
Rewritten
Dedupe hash
prn_302901373
Press Eligible
Yes
Press Eligible Reason
Huyett’s expansion into structural fasteners is a product and distribution announcement for industrial customers.
Source Name
Unknown Company
Original Summary

<p>Master distributor and manufacturer Huyett enters the structural market with an extensive inventory of parts, in stock and ready to ship in less-than-can quantities. MINNEAPOLIS, Oct. 14, 2026 /PRNewswire/ -- Huyett is proud to announce its entrance into the structural bolting market with...</p>

Image URL
https://mmx.prnewswire.com/media/MS2003338/Huyett-A325-Bolts.jpg?id=OA2971544&p=facebook
Content Hash (SHA-256, erste 32 hex)
69fb7dbab608a27e47c513f8effb801a
Introducing Chainguard Workspaces: Hardened, Hardware-Isolated Environments for Faster Agentic Development
Image File
Original HTML

Hardware-isolated, credential-free microVMs built from zero-CVE Chainguard OS Packages give security and platform teams a safe way to run fleets of agents at full speed

SEATTLE, Oct. 14, 2026 /PRNewswire/ -- Chainguard, the trusted source for open source, today announced Chainguard Workspaces, hardened microVMs that give every developer and coding agent their own secure environment, with no access to sensitive credentials and optional egress policies that block any connection a team has not approved. Because protection is built into the environment rather than left to the agent, security and platform teams can let agents run autonomously while limiting the blast radius of any compromise and keeping a signed record of everything each agent did.

The tradeoff between access and safety

Coding agents today run migrations, remediation campaigns, and refactors that last for hours, and most agents have the same access as the developer who launched them, right next to their credentials, cloud keys, and production systems. The controls meant to keep them in check, such as permission prompts and allowlists, depend on the agent's adherence to the rules. At the same time, many developers now run a dozen agents or more at once. Teams have to choose between giving agents enough access to be useful and accepting the risk, or locking them down behind approval prompts and spending their day clicking "allow."

"Right now teams are choosing between letting agents run next to their production keys or babysitting them through approval prompts all day. Neither one scales," said Dan Lorenc, CEO and Co-founder, Chainguard. "Workspaces gets rid of that tradeoff. Every agent gets its own hardened, isolated machine with nothing in it worth stealing, so you can let it run for hours and trust what comes out the other end."

A separate, hardened environment for every agent

Chainguard Workspaces is built for security and platform teams whose developers run fleets of coding agents. Workspaces run as remote microVMs that sync each developer's local working tree, so developers keep their editor and git workflow while execution happens off their machine. Because every agent gets its own isolated environment, dozens of agents can work in parallel without colliding, and long-running migrations, remediation campaigns, and refactors can run for hours with no one watching. Teams can safely run agent-generated or third-party code, give every developer a standardized environment drawn from their Chainguard catalog, and try many candidate fixes at once. Security teams get visibility into what the agent read, ran, and reached before approving agent use.

To meet security teams' needs, Workspaces has:

- Layers of defense: Workspace microVMs are built exclusively with zero-CVE Chainguard OS Packages, including FIPS-compliant toolchains. Dependencies are verified against the lockfile at runtime, so untrusted or tampered code can't execute.

- Exfiltration-safe by design: Real credentials are injected outside the workspace, so agents never hold them. Tools that need a credential on disk get an encrypted, short-lived stand-in that is useless if taken.

- Configurable egress controls: Optional network egress policies block unauthorized outbound requests, preventing a prompt-injected agent or compromised dependency from communicating with unapproved external systems.

- Total visibility into every run: Every credential call and network connection is logged in a tamper-proof record, and every run generates signed attestations of the exact environment, code changes, and check results.

Alongside those security controls, Chainguard Workspaces provides engineering teams with what they need to build faster with agents:

- Fast starts and resumes: Cache-hot microVM snapshots mapped to the exact repository and toolchain let teams launch new workspaces or resume idle ones in seconds.

- Instant local package loading: Dependencies load directly from local disk as defined by the lockfile, removing external registry fetches and download delays from the loop.

- Built-in completion validation with Chainguard Checks: Paired with Chainguard Checks (also launching today in Beta), agents run CI suites in context and keep iterating until checks pass. Tying the loop exit to verified results keeps incomplete or faulty code from being handed off.

- Human-in-the-loop: When an agent requires developer input, the Workspace stays active for 10 minutes before automatically suspending to a snapshot. Memory state, active processes, and warm caches are preserved with no ongoing compute spend while paused.

With Workspaces, Chainguard extends the secure-by-default foundation behind its open source software catalog to the environments where agents write and run code. As agent adoption outpaces security review, the shift from securing the agent to securing where it runs is becoming a requirement for enterprise teams.

"Banks, fintechs, and corporates across Australia rely on Cuscal to move money safely. For agent sandboxing, we need an environment where AI agents can iterate quickly without risking core systems. We're excited to work hand-in-hand with Chainguard as an early design partner to shape the future of software development end-to-end," Brad McCoy, Senior Manager, Cloud Platforms, Cuscal.

"IDC research shows that organizations rank AI-generated code and agentic development workflows alongside third-party software and open source packages as top software supply chain concerns. Addressing that risk means accounting for what an agent can access while it works, in addition to the code it writes. Agents running with developer-level credentials and broad network access extend the supply chain attack surface in ways that many traditional controls were not designed to address," said Katie Norton, Research Director at IDC. "Approaches that isolate agent execution environments, keep secrets out of the agent's reach, and maintain auditable records of agent activity, such as the approach Chainguard is taking with Chainguard Workspaces, are designed to support agentic development at scale while preserving control over the development environment."

Chainguard Workspaces is available now in Beta. For more information, visit: chainguard.dev/workspaces.

About Chainguard

Chainguard is the trusted source for open source. By providing engineers and AI agents with hardened, trusted, and production-ready artifacts, Chainguard helps organizations prevent AI supply chain attacks, increase engineering velocity while reducing toil, and maintain continuous compliance. Customers include Fortune 500 enterprises and global industry leaders, including Anduril, Canva, DocuSign, OpenAI, Public Storage, Snap Inc., and Snowflake. Chainguard is venture-backed by leading investors, including Amplify, IVP, Kleiner Perkins, Lightspeed Venture Partners, Mantis VC, Redpoint Ventures, Sequoia Capital, and Spark Capital.  For more information, visit: https://www.chainguard.dev/ 

Media Contact: Brittany Hendrickson, [email protected]

SOURCE Chainguard

Share this article
Class (B2B/B2C)
B2B
Ingest Status
Rewritten
Dedupe hash
prn_302907716
Press Eligible
Yes
Press Eligible Reason
Chainguard announced a security-focused developer product for enterprise teams.
Source Name
Introducing Chainguard Workspaces
Original Summary

<p>Hardware-isolated, credential-free microVMs built from zero-CVE Chainguard OS Packages give security and platform teams a safe way to run fleets of agents at full speed SEATTLE, Oct. 14, 2026 /PRNewswire/ -- Chainguard, the trusted source for open source, today announced Chainguard...</p>

Image URL
https://mmx.prnewswire.com/media/MS684620/Chainguard-Logo.jpg?id=OA3017484&p=facebook
Content Hash (SHA-256, erste 32 hex)
635a24c79841dd9a06ca864e087b09fc
Introducing Chainguard Libraries for Go and .NET: Secure Endpoints to Protect Organizations from Supply Chain Attacks
Image File
Original HTML

Chainguard Libraries now includes CVE remediation for JavaScript and Go; customers also receive protections from frontier AI-discovered zero-days once they are made public

SEATTLE, Oct. 14, 2026 /PRNewswire/ -- Chainguard, the trusted source for open source, today announced Chainguard Libraries for Go and Chainguard Libraries for .NET, adding coverage for two new language ecosystems that allow engineering teams and AI agents to safely pull Go and .NET dependencies without being exposed to the next supply chain attack. Chainguard Libraries also now offers CVE remediation for JavaScript and Go, which backports upstream fixes for critical- and high-severity vulnerabilities, helping teams where upgrading to the next version is not always immediately possible. Finally, Chainguard Libraries now protects customers from zero-day vulnerabilities, with fixes available the day a vulnerability is made public. Through Athena's crowdsourced threat intelligence, Chainguard Libraries customers receive novel patches for zero-day vulnerabilities that have been discovered by the world's largest institutions pointing frontier AI models at their applications.

Malware poses an increasing threat to open source dependencies

AI has escalated problems that have plagued open source language libraries for years, and malware is at the front of that shift. According to Chainguard's AI Exploit Gap report, 76% of cybersecurity leaders say their organization has experienced, or suspects it has experienced, an AI-driven attack in the last 12 months. Within open source registries, attackers are publishing malicious packages, hijacking trusted packages, and registering the names of packages that do not exist yet, knowing developers and AI agents will install them without a second look. At the same time, AI makes it possible for anyone to build and publish malicious packages, or find a way to gain improper access to internal systems by exploiting CVEs or newly discovered zero-day vulnerabilities. The risks are not new, but they are increasingly impossible to manage at scale as models become more capable and widely available.

"Attackers are counting on your developers and AI agents to trust every package they install," said Patrick Donahue, SVP of Product, Chainguard. "Chainguard Libraries removes the need for that trust. No malware gets in, CVEs get fixed even if you can't upgrade, and zero-days are patched on disclosure day. Prevention is the only defense that scales."

Protecting organizations from AI-level threats to open source software

Preventing malware from dependencies is only one part of a three-part problem. Organizations still need to worry about CVEs and zero-days that are becoming easier to discover and exploit as the capabilities of frontier AI models improve. Teams often pin dependencies to specific versions for stability, and CVEs build up in those versions over time. Meanwhile, frontier AI models are uncovering zero-days faster than open source maintainers can fix them. With today's announcement, Chainguard Libraries protects against all three threats across more of the languages organizations depend on:

- Introducing Chainguard Libraries for Go with CVE remediation: Chainguard Libraries for Go gives cloud and infrastructure development teams a secure endpoint to pull Go packages, limiting their organization's exposure to malicious modules and reducing the number of CVEs they need to remediate. Go Libraries come with built-in scanning for malware and greyware, a class of nefarious open source packages that traditional malware scanners miss. They also include configurable policies that allow teams to block packages that don't meet their security or compliance standards, and CVE remediation.

- Introducing Chainguard Libraries for .NET: Chainguard Libraries for .NET allows organizations building on top of the Microsoft and Azure ecosystems to trade NuGet for a secure-by-default Chainguard-managed endpoint, allowing them to safely pull dependencies without risking being compromised by the next supply chain attack. .NET libraries come with configurable policies and malware and greyware scanning.

- Enhancing JavaScript libraries with CVE remediation: Adding CVE remediation to Chainguard Libraries for JavaScript provides another layer of defense that reduces CVE risk. Backported fixes for critical- and high-severity CVEs allow engineering teams to shrink known vulnerability risk while strategically planning their next major version upgrade. The capability is built into the same endpoint that has blocked every malware attack that has hit npm this year.

- Providing zero-day protection for Chainguard Libraries for Java and Python: Chainguard Libraries for Python and Java now have artifacts that are remediated from frontier AI model-discovered vulnerabilities on the day they are publicly disclosed. This protection is powered by the crowdsourced threat intelligence of Athena, Chainguard's industry coalition for the orchestrated defense of open source software.

These advancements make Chainguard Libraries the most secure way to consume open source language dependencies. Chainguard Libraries helps organizations defend against the threats frontier AI models pose to open source software and to the AI software development lifecycle.

"Chainguard Libraries has shifted us from reacting to supply chain attacks to preventing them. We have immediate visibility into what's coming into our environment, but more importantly, malicious packages never reach us in the first place," said Kevin Fuller, CISO, Propio. "It's not just detection, it's prevention. With constant attacks on open source, that has given our team a world of peace."

Chainguard Libraries for Go and .NET are now available in Early Access. For more information, visit chainguard.dev/libraries.

About Chainguard

Chainguard is the trusted source for open source. By providing engineers and AI agents with hardened, trusted, and production-ready artifacts, Chainguard helps organizations prevent AI supply chain attacks, increase engineering velocity while reducing toil, and maintain continuous compliance. Customers include Fortune 500 enterprises and global industry leaders, including Anduril, Canva, DocuSign, OpenAI, Public Storage, Snap Inc., and Snowflake. Chainguard is venture-backed by leading investors, including Amplify, IVP, Kleiner Perkins, Lightspeed Venture Partners, Mantis VC, Redpoint Ventures, Sequoia Capital, and Spark Capital.  For more information, visit: https://www.chainguard.dev/

Media Contact: Brittany Hendrickson, [email protected]

SOURCE Chainguard

Share this article
Class (B2B/B2C)
B2B
Ingest Status
Rewritten
Dedupe hash
prn_302907708
Press Eligible
Yes
Press Eligible Reason
Enterprise cybersecurity product announcement for securing open-source software dependencies.
Source Name
Introducing Chainguard Libraries for Go and .NET
Original Summary

<p>Chainguard Libraries now includes CVE remediation for JavaScript and Go; customers also receive protections from frontier AI-discovered zero-days once they are made public SEATTLE, Oct. 14, 2026 /PRNewswire/ -- Chainguard, the trusted source for open source, today announced Chainguard...</p>

Image URL
https://mmx.prnewswire.com/media/MS684620/Chainguard-Logo.jpg?id=OA3017454&p=facebook
Content Hash (SHA-256, erste 32 hex)
f960c2f259206d78b8fd80ddf27e0c50
Semperis 2026 Ransomware Report Reveals Increases in AI-Driven Attacks and a Rise in Physical Threats Against Executives and Their Families
Image File
Original HTML

The study reveals AI is reshaping ransomware as repeat attacks, threats to employees and their families, and attacks on identity systems outpace recovery readiness.

HOBOKEN, N.J., Oct. 14, 2026 /PRNewswire/ -- Semperis, the identity-driven cyber resilience and crisis response company, today published results from its annual global ransomware report, highlighting that AI plays a significant role in the ransomware economy. In addition, hackers are increasingly threatening physical harm against companies' employees to extract ransom payments; in more than half the reported cases, the attackers followed through on those threats. Only organizations that were victimized by ransomware gangs in the past 12 months were included in the study.

"An attacker has one goal in mind: They want to extract something from you. And the only way they're going to do that is to make the cost of resisting their demands greater than the cost of giving in," said Chris Inglis, the first U.S. National Cyber Director and a Semperis Strategic Advisor. "Holding you at physical risk is the latest phenomenon because we've covered most of the other risks."

The 2026 Ransomware Risk Report, found that bad actors are threatening victims with psychological intimidation in nearly 25% of all attacks in the U.S., UK, France, Germany, Italy, Spain, Singapore, Canada and Australia. In 53% of cases, the victims reported that the hackers followed through on their threats; 23% of victims or family members were swatted; 25% of victims sought psychological and medical treatment because of the ransomware attack; and 24% of victims or families hired personal security.

"IT and cybersecurity staff are already dealing with high levels of stress," says Tim Beasley, Semperis Senior Incident Response Consultant. "A ransomware attack takes that to a whole new level. I have seen CISOs say, 'I'm out. I'm done. I can't do this. It isn't worth it.' I've seen people walk out the door because leadership thought they mismanaged something that caused the breach to occur. It all takes a mental toll."

Key Findings

- AI is changing the ransomware landscape. 

In 87% of attacks, threat actors weaponized artificial intelligence.

- Attackers increasingly threaten victimized companies' staff and their families. 

Overall, 40% of attacks involved psychological or physical threats against staff.

- Multiple attacks (and multiple payments) continue.

In nearly 70% of attacks, the ransomware victims were targeted multiple times; 31% made multiple payments to attackers.

- Identity infrastructure continues to be a prime target as identity recovery preparation lags.

All told, 87% of ransomware attacks targeted identity systems like Active Directory (AD), Entra ID, and Okta. But only about half the companies we surveyed have dedicated identity backups, automated identity recovery solutions, and identity-specific crisis response procedures.

"The bad guys are always evolving their tactics," said Mickey Bresman, Semperis CEO. "When the initial wave of ransomware attacks began, most focused on data encryption. Then, after data backup and recovery systems started gaining traction and enabling companies to resist ransom demands, we saw the double extortion: encryption coupled with data theft and threats to expose or sell that data. So, it makes sense that we'll continue to see attackers trying to find more ways to make victims pay."

Even though identity infrastructure is a prime target for threat actors, identity continues to be at risk in most organizations. In fact, nearly 75% of successful ransomware attacks targeted or exploited the identity system. Only 50% of companies maintain dedicated identity backup systems; and less than half automate identity system recovery. Shockingly, 40% of organizations' disaster recovery or crisis response plans don't include procedures for AD recovery.

"Identity is the coin of the realm. If an attacker can steal an identity, they're off to the races. Insider threats are not always a literal insider—a physical person who's abusing their authority," said Inglis. "Often, it's an internal person acting on an external attacker's behalf to abuse an insider's privileges. Sometimes it's a process that just runs amok. In every case, identity is the core issue."

The full Ransomware Risk Report can be found here: https://www.semperis.com/ransomware-risk-report/

About Semperis

Semperis is the identity-driven cyber resilience and crisis management company trusted by the world's largest enterprises and government agencies to protect critical identity systems. Purpose-built for multi-cloud and hybrid identity environments—including Active Directory, Entra ID, Okta, and Ping Identity—Semperis helps organizations prevent, detect, respond to, and recover from identity-based cyberattacks.

Modern cyberattacks are won or lost at the identity layer, where failures now escalate into full-scale business crises. Semperis' AI-powered platform unifies identity lifecycle defense and crisis management—hardening identity infrastructure, detecting and containing active threats, enabling rapid, trusted recovery, and supporting secure, out-of-band coordination when core systems are disrupted—all reinforced by a world-class identity forensics and incident response team.

As part of its mission to help organizations achieve true cyber resilience, Semperis supports the broader cyber community through the award-winning Hybrid Identity Protection (HIP) Conference and Podcast and free identity security tools including Purple Knight and Forest Druid. More than 1,200 organizations—including over 25% of the 100 largest U.S. companies—rely on Semperis. The company is privately held, headquartered in Hoboken, New Jersey, and serves customers in more than 40 countries.

Learn more: https://www.semperis.com

Follow us: Blog / LinkedIn / X / Facebook / YouTube

Media Contact:

Bill Keeler

Senior Director, PR & Comms

[email protected]

SOURCE Semperis

Share this article

Class (B2B/B2C)
B2B
Ingest Status
Rewritten
Dedupe hash
prn_302907731
Press Eligible
Yes
Press Eligible Reason
Company cybersecurity report on ransomware trends and organizational preparedness.
Source Name
Unknown Company
Original Summary

<p>The study reveals AI is reshaping ransomware as repeat attacks, threats to employees and their families, and attacks on identity systems outpace recovery readiness. HOBOKEN, N.J., Oct. 14, 2026 /PRNewswire/ -- Semperis, the identity-driven cyber resilience and crisis response company,...</p>

Image URL
https://mmx.prnewswire.com/media/MS1122565/Semperis-Logo-Logo-Logo.jpg?id=OA3017407&p=facebook
Content Hash (SHA-256, erste 32 hex)
3022b82ce7757489b871b2ff453b76db
Moxa Receives Prequalification from Saudi Energy for Industrial Networking and Computing Solutions
Image File
Original HTML

Moxa Receives Prequalification from Saudi Energy for Industrial Networking and Computing Solutions

TAIPEI, Oct. 14, 2026 /PRNewswire/ -- Moxa, a trusted leader in industrial communications and networking, is pleased to announce that it has received prequalification from Saudi Energy (Saudi Electricity Company (SEC) and National Grid (NG) , Saudi Arabia, for its Ruggedized Industrial Ethernet Switches, Industrial Next-Generation Firewalls, and Industrial Computers.

All three product categories have been approved and added to Saudi Energy's LOTAM (List of Technically Acceptable Manufacturers), enabling Moxa to provide an integrated industrial networking and computing solution for critical energy infrastructure applications, including Substation Automation (SA) and Advanced Metering Infrastructure (AMI).

Moxa's solutions can also support the migration and modernization of legacy substations, backed by extensive experience in upgrading legacy utility infrastructure worldwide.

The approval followed a rigorous prequalification process, including product testing at third party lab in the presence of Saudi Energy team, a factory visit, and proof-of-concept testing for various applications.

This prequalification strengthens Moxa's opportunity to expand its installed base across Saudi Arabia and the wider Middle East, particularly as the region's power sector continues to grow with the development of AI data centers and large-scale giga projects.

With extensive experience working with utility companies globally, Moxa remains committed to supporting the region with reliable, secure, and rugged industrial networking solutions.

Moxa sincerely thanks the Saudi Energy team for their support, collaboration, and trust in Moxa.

For more information reach us on [email protected]

About Moxa

Moxa is a leading provider of edge connectivity, industrial computing, and network infrastructure solutions for enabling connectivity for the Industrial Internet of Things. With over 35 years of industry experience, Moxa has connected more than 118 million devices worldwide and has a distribution and service network that reaches customers in more than 87 countries. Moxa delivers lasting business value by empowering industry with reliable networks and sincere service for industrial communications infrastructures. Information about Moxa's solutions is available at www.moxa.com.

The MOXA logo is a registered trademark of Moxa Inc. All other trademarks mentioned in this document are the property of their respective owners.

SOURCE Moxa Inc.

Share this article

Class (B2B/B2C)
B2B
Ingest Status
Rewritten
Dedupe hash
prn_302902517
Press Eligible
Yes
Press Eligible Reason
Industrial networking products prequalified for Saudi energy infrastructure applications.
Source Name
Unknown Company
Original Summary

<p>TAIPEI, Oct. 14, 2026 /PRNewswire/ -- Moxa, a trusted leader in industrial communications and networking, is pleased to announce that it has received prequalification from Saudi Energy (Saudi Electricity Company (SEC) and National Grid (NG) , Saudi Arabia, for its Ruggedized Industrial...</p>

Image URL
https://mmx.prnewswire.com/media/MS2005021/MoxaLogo_Tagline_Version.jpg?id=OA2994479&p=facebook
Content Hash (SHA-256, erste 32 hex)
793475d89c1ec86e0788544fc4283d8a
AI Needs a Governed Path, Not a Ban, Armor Founder Tells GovWare
Image File
Original HTML

AI Needs a Governed Path, Not a Ban, Armor Founder Tells GovWare

Chris Drake says AI should complete useful business work automatically within policy. CISOs can enable that autonomy by resolving data classification, owning routing rules and demanding auditable evidence.

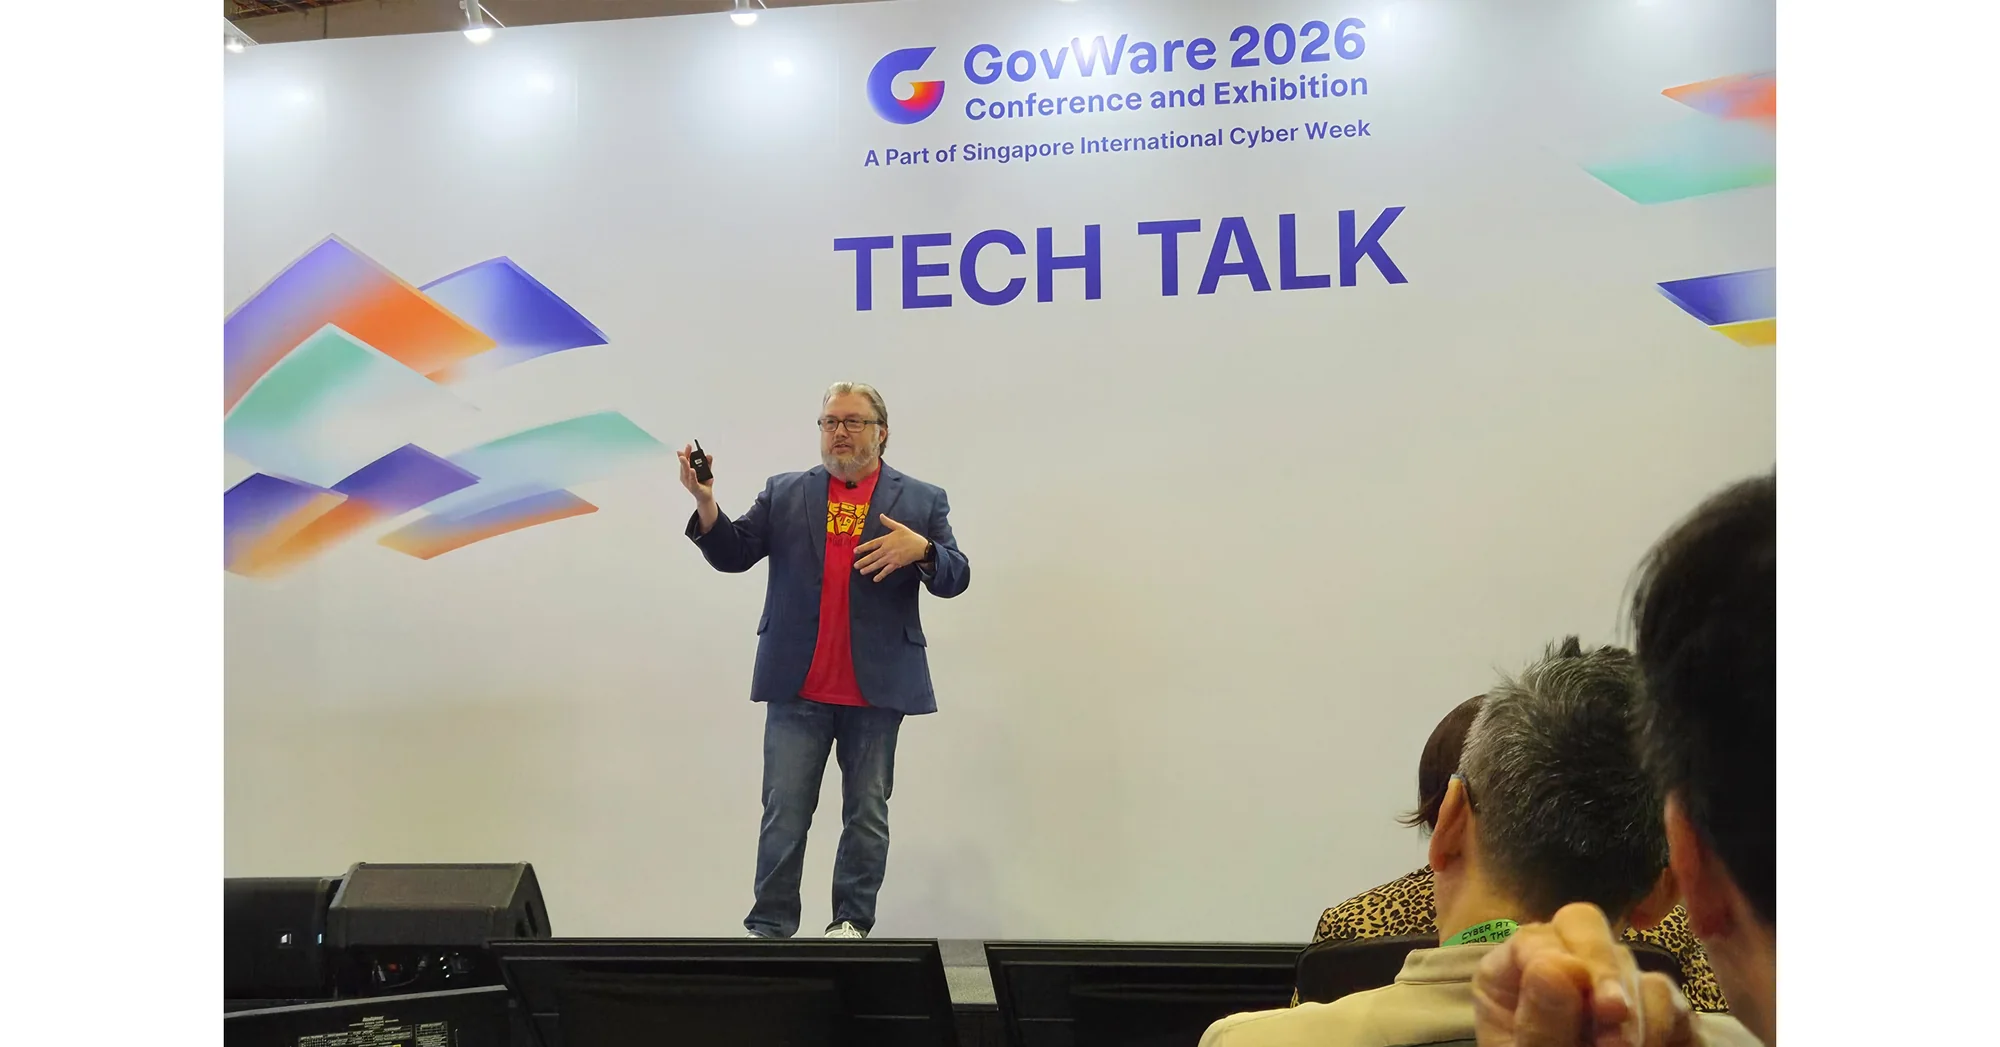
SINGAPORE, Oct. 14, 2026 /PRNewswire/ -- CISOs face pressure to get out of the way of AI innovation while keeping the business alive, Armor Founder and CEO Chris Drake told GovWare 2026 today. Leaders see a competitive risk in moving too slowly. Security leaders must also protect customer trust, contractual commitments, and operations. AI is already arriving through employees and the tools they use, often without a separate security decision. In his Tech Talk Spotlights session, "Once Again. AI Puts CISOs Between a Rock and a Hard Place," Drake argued for AI to complete useful business work automatically within policy, with CISOs setting the conditions for adoption and having the authority and evidence to enforce them.

"With the cloud, the CISO at least got a say. With AI, nobody asked. Banning it doesn't work, and ignoring it is how the breach report gets written," said Drake.

Drake contrasted AI with the cloud transition, when security could assess a provider and influence which applications and data left the corporate environment. AI can arrive inside existing browsers, productivity tools, and employees' machines without that checkpoint. Depending on permissions, an agent can read files, send data, and take actions. The risk can travel over an allowed connection even when the firewall works as configured.

After decades spent defending the perimeter, organizations must now examine the AI agents running on employees' machines. Drake highlighted specific local virtual machine visibility gaps: Anthropic documents that host endpoint detection and response (EDR) cannot inspect activity inside Cowork's local VM, while Docker documents that processes inside its local sandbox microVMs are invisible to the host. EDR alone cannot provide complete oversight; platform telemetry and network controls remain important. An employee clicking "Allow" does not settle whether the business approved the data access or processing.

Drawing on his conversations across APAC, Drake described the pressure on CISOs who report to the CIO or CTO sponsoring an AI rollout. He urged them to gain trust and lead the decision: agree on the business outcome, define what earns a yes and demand evidence that the controls and business result work. CISOs also need a written mandate to approve, restrict or pause AI use; a named executive who owns each risk exception and its expiration date; and an escalation path to the risk committee. These are decisions about the conditions for AI adoption, not approval of every routine AI action.

Suppliers extend that exposure. A vendor's use of another AI provider to process an organization's data introduces fourth-party risk. Organizations need evidence of the providers involved, where data is processed, what is retained and which contractual protections apply. Protiviti's February 2026 AI Pulse Survey found that 47% of large organizations reported incomplete visibility into employees' use of AI tools. A useful, approved AI path can reduce the incentive to work around security, while discovery and supplier oversight remain essential.

Drake said data classification has moved from nice-to-have to must-have. Organizations must know what their data contains, who owns it and how it may be used. Classification, ownership, permitted use and auditability provide the basis for rules that systems can enforce automatically. "AI cannot safely use data you cannot govern," he said. Once that foundation is established, organizations should own the routing policy. Use approved external models when data policy permits and private execution when required. Task complexity, model capability, business needs and cost then guide the choice among permitted options. AI can complete authorized work automatically, with records of the data accessed, policy decisions, models, routes, actions and outcomes. Those receipts let the organization reconstruct what happened without making a person approve every step.

Armor, a provider to regulated industries since 2009, faced the same challenge. Drake said the company was concerned about sending customer data through public AI services where the controls and audit evidence could not meet its customer commitments. It built a governed AI platform for its own operations, now Sovereign AI, and runs its business on it.

Drake closed with the principles behind Sovereign AI: know the data, preserve model choice, own routing policies, control actions and demand full auditability. Give the whole company useful, approved AI so employees have less reason to turn to shadow AI. He called for powerful agents and their credentials to run in governed, isolated, auditable environments, with scoped access, rather than on employees' laptops.

Before granting an AI tool access, he urged CISOs to ask three questions:

- What can it touch?

- Where can it send?

- Can we control what it does?

His message to CISOs was: "Yes. With rules. With authority. With evidence." The presentation is available at https://www.sovai.com/govware26.

Armor is demonstrating Sovereign AI at Booth A22 through October 15. Press and analyst briefings with Drake are available on-site and virtually; requests go to the media contact below.

ABOUT SOVEREIGN AI

Sovereign AI is the governed AI work platform for the whole company, built by Armor. One control layer for every model, every team, and every dollar, inside your walls, under your rules. Armor has spent 17 years securing regulated industries, protecting over 1,700 organizations across 40+ countries held to the highest compliance bars in the business. Sovereign AI is what that experience looks like as a product. Learn more at sovai.com.

ABOUT ARMOR

Since 2009, more than 1,700 organizations in 40+ countries have relied on Armor to protect regulated data in the public and private cloud. AI is the next risk, so Armor built Sovereign AI to bring that same protection and compliance to how organizations use AI in the workplace: a fully governed platform that lets them leverage AI without creating undue risk to their data and their regulatory obligations. For more information, visit armor.com and sovai.com and follow us on LinkedIn.

Media Contact

Michele Glassman

Marketing Director, Armor

[email protected]

SOURCE Armor Defense Inc

Share this article

Class (B2B/B2C)
B2B
Ingest Status
Rewritten
Dedupe hash
prn_302907936
Press Eligible
Yes
Press Eligible Reason
Company announcement about a governed AI platform and enterprise security guidance for CISOs.
Source Name
Unknown Company
Original Summary

<p>Chris Drake says AI should complete useful business work automatically within policy. CISOs can enable that autonomy by resolving data classification, owning routing rules and demanding auditable evidence. SINGAPORE, Oct. 14, 2026 /PRNewswire/ -- CISOs face pressure to get out of the way...</p>

Image URL
https://mmx.prnewswire.com/media/MS2012958/Armor-Defense-Inc-TT-PR-image-Drake.jpg?id=OA3017763&p=facebook
Content Hash (SHA-256, erste 32 hex)
e44fc6eba6738c407314f5879f769e01